8th October, 2026
- Issuer, Holder and Verifier: Who Does What
- What a Verifier Learns at the Point of Check
- Where EveryCRED Fits in Government Work
- Three Credential Checks, Role by Role
- What Stays With the Issuing Office
- Open Standards Behind Each Credential
- What Is Available Now
- How Carahsoft Fits When Your Agency Is Ready to Buy
- Plan Your First EveryCRED Credential


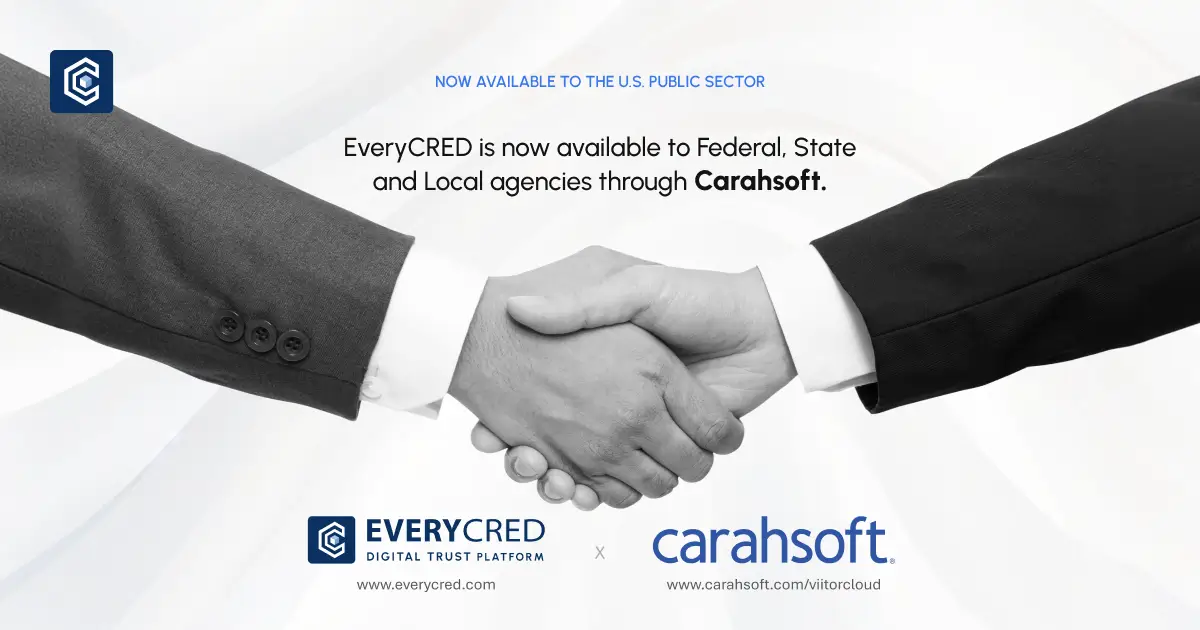
US federal, state, and local agencies can now buy EveryCRED, our platform for credential management and verification, through Carahsoft.
ViitorCloud, the company behind EveryCRED, announced the partnership on October 1, 2026. Carahsoft serves as ViitorCloud’s Master Government Aggregator®, so EveryCRED is available through Carahsoft’s reseller partners and the NASA SEWP V, ITES-SW2, NASPO ValuePoint, and OMNIA Partners contracts listed in the official announcement.
Issuer, Holder and Verifier: Who Does What
A credential is a signed record of a fact that an authority stands behind. Agencies call these by different names: a permit, a license, a pass, an ID, or an authorization. Each credential involves three roles: the issuer who grants it, the holder who carries it, and the verifier who checks it. Each role has a different job.
Issuer
An issuer is the authority that grants a credential and can withdraw it. In a US agency, that might be a licensing office, a facility security team, or a contracting office. Issuers can be internal teams or outside organizations. Outside issuers are usually verified through KYB, a check that confirms a business is what it claims to be.
On EveryCRED, an issuer decides what each credential contains, who receives it, and when it should be revoked. Revocation means withdrawing or cancelling a credential. Credential management on EveryCRED covers each stage an issuer controls: issue, revoke, reissue, and transfer.
Holder
A holder is the person a credential describes, or the owner of a business it describes. Holders join by invitation, with or without an identity check, or through their organization’s existing sign-on.
Holders can keep credentials in an app the organization already provides, in any standards-compliant digital wallet, or in a white-label wallet carrying the organization’s own branding.
Verifier
A verifier is whoever checks the credential at the point of use. That could be a guard at a gate, an access point at a door, or a caseworker reviewing an application. On EveryCRED, a verifier checks credentials through the verifier app, registered gate hardware, access points, or APIs. In open settings, where verifiers are not part of one organization, a simple app or web page is enough.
Administrators run the platform for the agency. Each administrator’s access depends on their assigned role.
What a Verifier Learns at the Point of Check
A verifier usually cannot call the issuing office in the moment. With paper cards, PDFs, and phone calls, a verifier may never learn that a permission was withdrawn.
When a credential is checked on EveryCRED, the verifier learns two facts:
- Whether the credential is genuine. A forged or altered credential fails because it does not carry a valid signature from the issuer.
- Whether it is still valid right now. Each check returns the credential’s live status, including revocation.
When a Credential Is No Longer Valid
A credential can stop being valid in more than one way. EveryCRED handles each of these:
- Revoked by the issuer. An issuer withdraws a credential once, and it fails at every point where it is checked after that.
- Holder removed from HR records. When a holder is removed from the HR system, their credentials are revoked automatically.
- Issuer itself revoked. If an issuer is itself revoked, the credentials it issued can be revoked too.
Audit Records for Each Check
Every verification is logged with who checked, where, when, and the result. Agencies can export these records to their existing monitoring and audit tools through OpenTelemetry, an open standard for sending logs between systems.
Where EveryCRED Fits in Government Work
For US public sector buyers, the October 1 announcement names six EveryCRED workflows:
- Contractor access validation: check that contractors and outside partners meet security requirements before they get access.
- License-based access control: grant access only after a real-time check that a person’s license is valid.
- Privileged role verification: confirm that staff in sensitive roles hold the qualifications that role requires.
- Grant and benefit eligibility: check that applicants are eligible, which helps reduce fraud.
- Inter-agency credential exchange: share and verify credentials securely across agencies.
- Supply chain and vendor integrity: verify suppliers and vendors throughout the procurement process.
Three Credential Checks, Role by Role
These examples are illustrative. They show how the three roles work together in common agency tasks. They do not describe a specific customer deployment. Our public sector page covers more government use cases.
Contractor Authorization
A facility needs proof that a contractor is approved for a site and has finished the required safety training.
- Issuer: a contracting office issues a site permit, and a training provider issues a qualification. More than one issuer can sign a credential on EveryCRED, and credentials can be linked when a check needs both.
- Holder: a contractor who carries both credentials on a phone.
- Verifier: a guard or access point checks both at entry.
- If it is no longer valid: when the contract ends, the contracting office revokes the permit, and any later check at the gate fails.
License Verification
An agency grants access to a site or system only to people with a current professional license.
- Issuer: a licensing authority issues the license as a credential.
- Holder: a licensed professional.
- Verifier: an agency access point or system, which checks the license in real time before granting access.
- If it is no longer valid: when the licensing authority revokes the license, the next check fails, and access is not granted. A copy saved in the holder’s wallet no longer passes verification.
Eligibility Check
A benefits program needs to confirm a fact that another office has already established.
- Issuer: an office that has confirmed the fact issues an attestation, which is a signed statement that the fact is true.
- Holder: an applicant.
- Verifier: a caseworker reviewing the application.
- If it is no longer valid: when the issuing office revokes the attestation, the caseworker sees that at the next check.
EveryCRED supports SD-JWT, a credential format that allows selective disclosure, which helps protect applicant privacy. With it, the applicant shares only the fields the caseworker needs.
Eligibility checks are also a fraud control. In 2024, the US Government Accountability Office estimated that the federal government loses between $233 billion and $521 billion a year to fraud, based on data from fiscal years 2018 to 2022. Checking eligibility facts against the office that confirmed them is one of the controls an agency can use.
What Stays With the Issuing Office
EveryCRED does not decide who should hold a credential. That decision stays with the issuing office, along with its policies, approval steps, and records.
EveryCRED also works with the systems an agency already runs:
- Identity: each credential is tied to an identity from Microsoft Entra ID, Google Workspace or another enterprise identity system. For people and businesses outside the agency, identity can come from a KYC or KYB provider.
- Records: credential details can come from HR systems, workforce scheduling tools such as Workday, CRM and visitor management systems.
- Security: EveryCRED adds a check on credentials. It does not replace an agency’s wider security controls.
Open Standards Behind Each Credential
EveryCRED issues credentials as W3C Verifiable Credentials and supports SD-JWT. Because both are open standards, any compliant wallet or verifier can work with the credentials. An agency does not need EveryCRED apps to check them. EveryCRED runs in a public or private cloud.
What Is Available Now
EveryCRED’s core credential management platform is live today:
- issuance and instant verification with real-time revocation status
- verifier app and APIs
- identity binding, data from systems of record, and automatic revocation
- credentials signed by more than one issuer, and linked credentials
- delivery to the organization’s own app, standards-compliant wallets and white-label wallets
- audit export through OpenTelemetry
How Carahsoft Fits When Your Agency Is Ready to Buy
Carahsoft makes EveryCRED available to US public sector buyers through its reseller partners and these contracts:
- NASA SEWP V: NNG15SC03B and NNG15SC27B
- ITES-SW2: W52P1J-20-D-0042
- NASPO ValuePoint: AR2472
- OMNIA Partners: R240303
Contract periods and state-level entries change over time, so procurement teams should check the EveryCRED contract list on Carahsoft before starting a purchase. For quotes and contract questions, use Carahsoft’s EveryCRED page.
Contract availability gives an agency a way to buy EveryCRED. It does not mean a US government body has endorsed or deployed EveryCRED. Each agency runs its own evaluation, security review, and approval before buying.
Plan Your First EveryCRED Credential
Which credential does your office issue that someone still checks by hand or by phone? Tell us what it is, who checks it, and what should happen when it is withdrawn. Our first step with a new client is a scoping session on one credential and one point of verification, which leads to a pilot. Contact the EveryCRED team to set up that session.